December 2, 2025
9:30 PM - IST
Enterprises entered 2025 with expanded security budgets, AI experimentation mandates, and accelerated cloud transformation programs. Yet as the year progressed, many security leaders discovered that investment velocity did not automatically translate into resilience maturity.
The governance gap widened.
In this recently concluded webinar, QKS Group analysts examined the defining cybersecurity shifts of 2025, where enterprise security programs struggled under AI-augmented threat pressure, and what structural priorities will define leadership agendas in 2026. Drawing on SPARK Matrix evaluations, ongoing advisory engagements, and proprietary buyer intelligence, the session translated market signals, architectural transitions, and CISO operating model changes into actionable guidance for senior security leaders.
The webinar delivered a research-driven briefing on the inflection point facing cybersecurity leadership. Participants gained clarity on why traditional security architectures strain under AI-enabled adversaries, how regulatory acceleration is reshaping board oversight, and what execution shifts CISOs must implement to move from reactive defense to governed resilience in 2026.
Why 2025 Redefined Cybersecurity Leadership: Analysis of how AI-driven attack automation, expanding digital ecosystems, and fragmented global regulatory frameworks elevated cybersecurity from a technical control function to a board-level accountability mandate.
Where Security Programs Struggled Under Scale: Examination of structural choke points including AI-amplified alert fatigue, identity sprawl across hybrid architectures, tool fragmentation, and operational complexity introduced by rapid cloud expansion.
The Hidden Risk of AI Acceleration: Assessment of how generative AI simultaneously strengthened detection capabilities while expanding attack surfaces, increasing adversarial sophistication, and creating governance blind spots within enterprise environments.
What Forward-Looking CISOs Are Doing Differently: Insights into how leading organizations are centralizing policy orchestration, converging identity and detection layers, embedding AI governance frameworks, and aligning security KPIs directly with enterprise risk appetite.
Investment and Architecture Priorities for 2026: Evaluation of budget reallocation trends, shifting from point solutions to platform consolidation, from perimeter defense to identity-first models, and from static controls to adaptive, intelligence-driven architectures.
Leadership Operating Model Shifts: Discussion on the evolution of the CISO role toward enterprise risk integrator, requiring deeper alignment with CIOs, boards, and business units to ensure cybersecurity supports operational continuity and digital growth.
Analyst Recommendations & Strategic Guidance: Practical recommendations for strengthening resilience frameworks, optimizing security talent structures, governing AI-enabled environments, and designing architectures capable of sustaining continuous threat evolution in 2026.
This session was designed for senior security and technology leaders responsible for enterprise risk governance, resilience strategy, and cybersecurity architecture transformation.
Viewers gained exclusive access to QKS Group's forward-looking Security Leadership Outlook 2026, supported by proprietary research intelligence and real-world advisory insights. The discussion provided clarity on where security programs are structurally vulnerable, what architectural and governance shifts are underway, and how enterprise leaders can confidently transition into 2026 with stronger resilience, measurable execution control, and board-aligned security strategy.
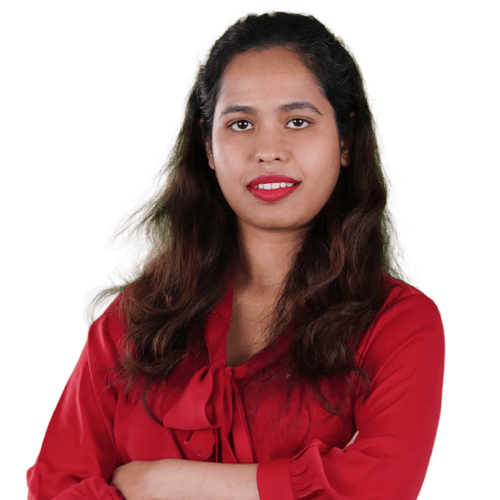
Associate Director & Principal Analyst
Sofia Ali serves as an Associate Director - Research at QKS Group, where she oversees the information security global strategic market outlooks, market insight reports, technology and user-survey guides, SPARK Matrix Analysis, and consulting assignments. Her expertise primarily spans identity & access management, managed security services and related areas. Sofia leads both independent research and consulting projects while also collaborating closely with a team of analysts. She has partnered with clients across diverse industries and regions, contributing to consulting engagements in areas like technology architecture planning, cloud transformation, vendor selection strategies, and operational due diligence. Beyond her core responsibilities, Sofia is actively involved in industry events, conferences, webinars, and talk shows featured on various social media platforms, where she shares her insights and engages in thought leadership conversations with industry experts and peers.

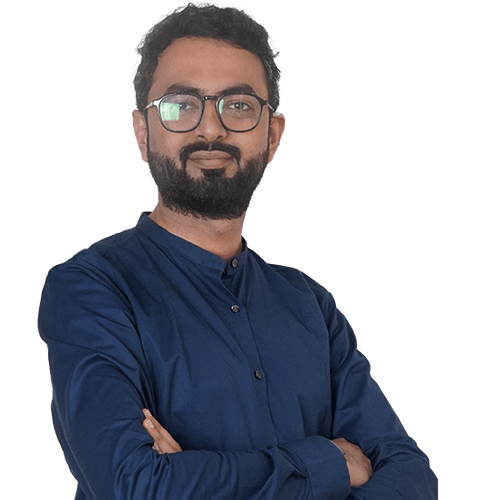
Senior Analyst -OT Security
Kunal Kumar is a Senior Analyst at QKS Group, specializing in cybersecurity with a strong focus on threat detection and response and operational technology (OT) security. His expertise spans key domains including Digital Threat Intelligence Management (DTIM), Security Orchestration, Automation and Response (SOAR), Security Information and Event Management (SIEM), Network Detection and Response (NDR), Extended Detection and Response (XDR), and Insider Risk Management (IRM), along with OT, ICS, and connected medical device security. With a strong foundation in market intelligence and cybersecurity research, Kunal plays a pivotal role in tracking industry trends, analyzing evolving threat landscapes, and evaluating vendor capabilities across global markets. He leads competitive benchmarking initiatives and is actively involved in positioning leading cybersecurity vendors within the SPARK Matrix, delivering data-driven insights that support strategic decision-making for both technology providers and enterprise buyers. Kunal’s work involves conducting in-depth primary and secondary research, engaging with cybersecurity vendors and end-users, and synthesizing complex technical and market data into actionable intelligence. He regularly authors research reports, thought leadership articles, and conducts webinars on emerging cybersecurity trends, helping organizations understand technology adoption patterns, market dynamics, and innovation trajectories. In addition to research, he collaborates closely with clients and vendors, supporting go-to-market strategies, customer engagement initiatives, and vendor positioning. His ability to bridge technical depth with market perspective enables stakeholders to make informed decisions in an increasingly complex and rapidly evolving cybersecurity ecosystem.

