Quantified risk, regulator-mapped gap registers, and time-boxed uplift sprints — grounded in SPARK Matrix™ research, delivered with your team, evidenced at every gate.
I have a regulator and a deadline
DORA
NIS2
NYDFS 500
SEC
FCA / PRA
APRA CPS 234 + CPS 230
MAS TRM
RBI
SEBI
EU Digital Operational Resilience Act
Evidence pack for entities in scope: ICT risk management, incident reporting, third-party register, resilience testing.
EUROPEAN UNION · READINESS SPRINT S-01
I want resilience beyond the audit
The six-stage journey: quantified diagnostic, prioritised strategy, target architecture, control governance, implementation, and continuous proof — nine domains, one spine.
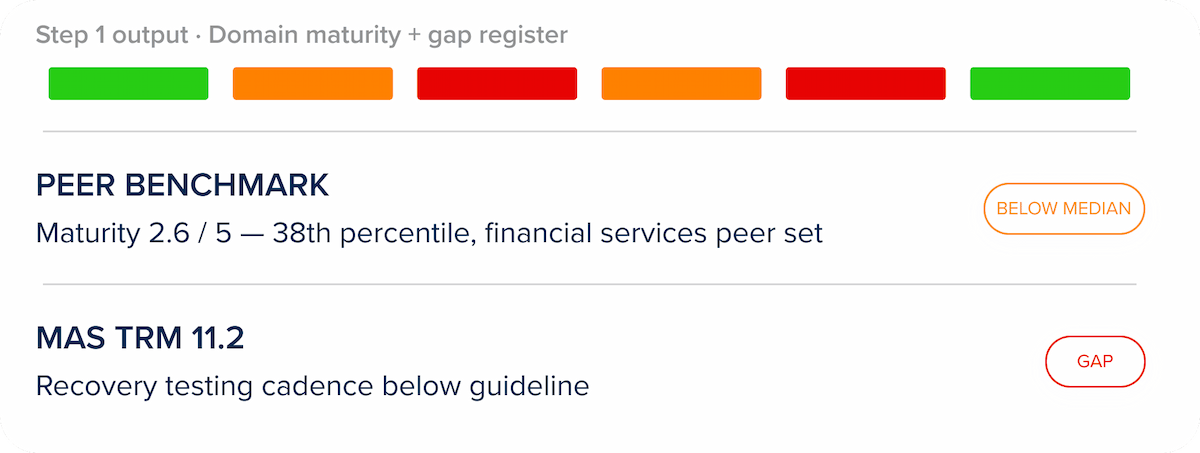
Illustrative Sample*
Not a consulting engagement with a report at the end — a platform that quantifies, ranks, and evidences your resilience decisions continuously. Six surfaces, one spine.
Risk Quantification
Exposure in dollars, traced per domain
Gap Intelligence
Obligation-level registers that update as regulations do
Decision Intelligence
Computed next-dollar investment ranking
Sprint Library
Exposure in dollars, traced per domain
Vendor Intelligence
Landscapes resolved from live SPARK research
Continuous Evidence
Evidence freshness, maturity milestones, attestation timelines
Cyber never stops — neither does the intelligence. Maturity re-scores, registers track regulatory change, evidence ages visibly, and the next-dollar ranking recomputes as your estate moves. Continuous decision intelligence — your tooling does the monitoring.
Resilience Sprint Library
Eleven outcome-named sprints — each a five-gate co-build with your security team, each ending in an artifact you can hand a regulator, a board, or an auditor. Durations computed from risk and scope, never promised flat.
S-01
Regulatory Readiness
Audit-ready against your regulator — gap register closed, evidence packaged, attestation signed
Gap Register
Evidence Pack
Attestation Memo
90-Day Close Roadmap
RISK M
S-02
Ransomware & Recovery Readiness
Know you can take the hit: recovery tested, RTO/RPO evidenced, crown jewels covered
Recovery Test Report
RTO/RPO Evidence
Crown-Jewel Coverage Map
RISK M
S-03
Incident Response Playbook + Tabletop
A tested playbook, not a shelf document — tabletop run, gaps dispositioned
IR Playbook
Tabletop Report
RISK M
S-04
SOC Visibility Uplift
See what you're missing: telemetry coverage mapped, detection gaps closed in priority order
Coverage Map
Gap Register
Tool Rationalisation (In-Platform)
90-Day Roadmap
RISK M
S-05
Zero Trust Identity — Phase 1
Identity as the new perimeter: privileged access controlled, phase-1 architecture live
Identity Architecture Blueprint
PAM Evidence
Phase Plan
RISK M
S-06
Third-Party Risk Uplift
Your suppliers, evidenced: tiered register, assessed criticals, monitoring stood up
Supplier Register
Monitoring Runbook
RISK M
S-07
Cloud Posture Uplift
Cloud misconfigurations found, fixed and kept fixed — baseline to managed state
Posture Baseline
Remediation Register
Guardrail Policies
90-Day Roadmap
RISK M
S-08
Data Protection Uplift
Know where the sensitive data is and prove it's controlled
Data Map
Control Coverage
RISK M
S-09
Cyber Risk Quantification
Cyber risk in dollars the board can act on — quantified, traced, defensible
Quantified Risk Pack
Investment Options
Board Deck
RISK L
S-10
AI Security & GenAI Governance Readiness
Your AI estate governed: shadow AI discovered, LLM guardrails set, model risk registered
Shadow-AI Inventory
LLM Guardrail Set
Model Risk Register
GenAI Usage Policy
RISK M
S-11
Threat Intelligence Uplift
Intelligence your SOC actually uses: PIRs defined, sources rationalised, wired into detection and response
PIR Set
Source Rationalisation
Detection/IR Integration Runbook
RISK M
Domain Transformations
Every transformation starts as a sprint and expands through the six stages, scoped to one domain. The sprint proves it in weeks; the program engineers it to stay.
SOC Transformation
ENTRY: S-04 SOC VISIBILITY UPLIFT
EXPANDS: ARCHITECT → EXECUTE → SUSTAIN
Identity Security Transformation
ENTRY: S-05 ZERO TRUST IDENTITY PH.1
EXPANDS: ARCHITECT → GOVERN → EXECUTE
Cloud Security Transformation
ENTRY: S-07 CLOUD POSTURE UPLIFT
EXPANDS: ARCHITECT → GOVERN → SUSTAIN
Data Protection Transformation
ENTRY: S-08 DATA PROTECTION UPLIFT
EXPANDS: GOVERN → EXECUTE → SUSTAIN
Incident Response Transformation
ENTRY: S-03 IR PLAYBOOK + TABLETOP
EXPANDS: EXECUTE → SUSTAIN
Cyber Recovery Transformation
ENTRY: S-02 RANSOMWARE & RECOVERY
EXPANDS: EXECUTE → SUSTAIN
Threat Intelligence Transformation
ENTRY: S-11 THREAT INTEL UPLIFT
EXPANDS: EXECUTE → SUSTAIN
Don't see your domain?
One engine underneath: a transformation is its entry sprint plus the six-stage journey scoped to the domain — same gates, same evidence discipline, program-length horizon.
We Help You Implement
Every sprint runs the same five gates. QKS authors the designs and holds the gates; your security team builds; nothing passes without evidence. Gate weeks are computed from risk tier — they always sum to the sprint's timeline.
G-1
Scope + evidence access
Scope definition, domain map, evidence-source checklist, success criteria.
SIGNED: SPRINT OWNER
G-2
Control & architecture design
Target control set, regulator mapping, risk-acceptance notes — designed by QKS.
SIGNED: YOUR CISO
G-3
Implement — co-build
Your team builds to the design; QKS gates conformance and dispositions every deviation.
GATED: DEVIATION LOG CLEAN
G-4
Validate & evidence
Test or tabletop executed; evidence pack assembled and verified against scope.
SIGNED: SPRINT OWNER + CISO
G-5
Attest / handover
Attestation memo or handover runbook — and the expansion path into the domain journey.
SIGNED: YOUR CISO
What We Do
Design the controls and architecture, hold the gates, validate the evidence, and stand behind the technical calls — practitioners in the build, not a deck at the end.
What We Don't
We are not an MSSP and not a systems integrator — we don't run your SOC or resell tools. Your team keeps the capability; when you need managed services, we'll say so and point you to people who do them well.
Security Decision Intelligence
The diagnostic quantifies your exposure in dollars, scores maturity across nine domains, and traces architectural dependencies — then ranks where investment moves risk the most. Not another maturity PDF: an investment order you can defend.
Identity
Cloud Security
DSPM
AI Security
Recovery
SOC / Detection
CNAPP
Exposure Mgmt
Third-Party Risk
Next-Dollar Ranking
Recovery
Largest traced exposure share vs lowest domain maturity — recovery testing gap compounds every other risk
SOC / Detection
Telemetry coverage gaps block validation of downstream controls — architectural dependency
Identity
High exposure share; prerequisite for Zero Trust phase sequencing
Security Vendor Intelligence
Every sprint's tooling resolves through the research, not a reseller margin. Follow one through:
SPRINT
SOC Visibility Uplift
See What You're Missing
→
CAPABILITIES
Detection · Response · Threat Intel · Exposure
Scoped To Your Gaps
→
SPRINT
SOC Visibility Uplift
See What You're Missing
→
VENDOR LANDSCAPE
Leaders & Emerging Challengers, Per Category
Resolves In-Platform · Refreshed Every Matrix Cycle
The firm that runs your assessment shouldn't be selling you the remediation. We don't. Independent selection is structural — QKS holds no reseller margin on any tool it recommends.
Where Resilience Breaks Down
Six places security programs stall — each mapped to the stage that closes it.
01
Risk nobody can quantify
Maturity scores without dollar exposure — so security competes for budget with adjectives.
Closed by
Diagnose — quantified ALE, traced to scenarios
02
Priorities set by the loudest vendor
Investment follows the last briefing, not the largest exposure or the dependency order.
Closed by
Strategise — computed next-dollar ranking
03
Forty tools, no architecture
Overlapping controls nobody rationalised; coverage gaps hiding between products.
Closed by
Architect — target architecture + tool rationalisation
04
Controls that exist on paper
Implemented ≠ operationalised. The audit finds the difference before you do.
Closed by
Govern — control operationalisation + ownership
05
Advice with a margin attached
The same firm that runs the assessment sells the remediation — and the tools.
Closed by
Independent selection — no reseller margin, ever
06
Improvement nobody can prove
Spend goes up; evidence of risk reduction doesn't. Renewal conversations get harder every year.
Closed by
Sustain — measured maturity + evidenced outcomes
What's Included In Your Free Assessment · No Cost
Three things land in your inbox
A complete picture — not a teaser PDF. Calibrated to the domains you selected.
01 · REPORT
Your Cyber Resilience Report
Pillar-level maturity scores across all 7 ETF pillars, with a Gap Register that maps directly to the initiatives you picked above.
9-domain assessment · Board-ready
02 · BENCHMARK
APAC Peer Benchmark
See where you sit against 200+ APAC enterprises by domain and sector — what separates the top quartile in your market from the rest.
SG · AU · IN · HK cohorts
03 · WORKSHOP
Free Deep-Dive Workshop
A QKS principal analyst walks your team through your top exposures, prioritises the next 90-day moves, and bridges you to the relevant stage.
Live · With our advisors
QKS benchmarks resilience maturity across 450+ enterprises in 18+ countries.
See SPARK Plus in Action
Every stage of your resilience transformation, purpose-built and connected. Here's what your team actually works in.
Diagnose
Strategise
Architect
Govern
Execute
Sustain

Practitioners, Not Just Analysts
QKS advisors are former CISOs, security architects, and resilience leads — not junior researchers. They bring delivery credibility to every engagement, every stage, every conversation.
Former C-suite operators
25+ years avg experience
APAC-native coverage
Andrew Aken
AVP – Research
Dr. Andrew Aken is a seasoned cybersecurity and technology leader with over two decades of experience spanning software engineering, enterprise security architecture, academia, and executive leadership. With Bachelor’s and Master’s degrees in Computer Science from Southern Illinois University (SIU) and a PhD in Business Administration specializing in Management Information Systems, he brings a rare blend of deep technical expertise and business-aligned security leadership.
Vijay Mohan Kamarthi
Associate Vice President - Information Security
Vijay Mohan Kamarthi serves as Associate Vice President – Information Security at QKS Group, leading cybersecurity advisory, governance, and enterprise security transformation initiatives across global enterprise and regulated industry environments. With deep expertise spanning cybersecurity strategy, security architecture, governance, risk and compliance (GRC), cyber resilience, and cloud security transformation, he works closely with CISOs, enterprise technology leaders, and security vendors to support strategic security modernization, operational resilience, and governance-driven transformation programs.
Anandh Ramaswamy
Practice Director
Anandh Ramaswamy is a Practice Director at QKS Group, leading research and advisory engagements across enterprise technology markets. He works closely with technology vendors and enterprise leaders to deliver market intelligence, competitive analysis, and strategic guidance that inform technology investment and growth decisions.
Sanjeevi C Ramachandran
AVP / Lead Analyst – Enterprise Research, Advisory & Consulting
Sanjeevi Cuddalore Ramachandran leads enterprise research, advisory, and consulting initiatives at QKS Group across digital transformation, enterprise applications, and governance-driven execution frameworks. With over 25 years of experience spanning ERP, SaaS, cloud platforms, and enterprise portfolio transformation, he works with enterprise IT leaders, product vendors, and consulting partners to assess enterprise technology platforms, define execution maturity benchmarks, and inform platform selection, implementation governance, and value realization across manufacturing, energy, oil & gas, BFSI, education, government, public sector, and technology ecosystems.
Divya Baranawal
Vice President & Principal Analyst
Divya Baranawal is part of the global research and consulting team at QKS Group. As Vice President and Principal Analyst she heads the BFSI and Financial Crime & Compliance domains and is responsible for leading global strategic market outlook, competitive intelligence, market intelligence, and user intelligence. In this role, she leads multiple engagements with technology vendors in the areas of- technology consulting and growth advisory. She is also responsible for leading various custom advisory projects- including go-to-market strategies, value propositions, thought leadership assets, in-depth analysis of market trends, competitive landscape, market share & market forecast analysis and end-user insights.
Narayan Gokhale
Vice President & Principal Analyst
Narayan Gokhale is working as an ‘Vice President & Principal Analyst – Research and User Consulting with QKS Group. He leads research, sales and marketing of various domains, such as, IoT & Digitalization, Procurement, Supply Chain Management, Retail and HR Tech. He leads a large team of analysts and guides them in various research, consulting and advisory assignments. He is also responsible for maintaining client relations and leads subscription sales & custom consulting projects. He front-ends client-facing activities through face-to-face as well as virtual meetings.
Join 350+ enterprises across 18 countries using SPARK Plus to govern, build, and scale AI with confidence.